 PH
Node.js Security Releases (Oct 21, 2026): Update na sa 22.23.4, 24.22.1, o 26.12.1
Mga ka-PHC na may Node.js apps o servers, time to ρá†ch. The Node.js project shipped security updates for the 22.x, 24.x, and 26.x lines on October 21, 2026. 10 issues yung na-fix, at 4 dun rated high, kasama yung Brotli decoder bug na pwedeng mauwi sa remote code execution. Update in 6 steps
 Official advisory for the October 21, 2026 security releases · Image: OpenJS Foundation and Node.js contributors, from the official Node.js blog
Kailangan mo muna
- Terminal access sa machine o server na may Node
- Alam mo kung paano naka-install yung Node mo: official installer, version manager (like nvm), Linux package manager, o Docker image
- Access sa Dockerfiles at CI/CD config mo, kung meron
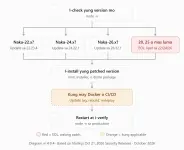
 Which version to install based sa current line mo · Diagram made for this thread, based on the Node.js October 21, 2026 security advisory
Paano mag-update
- Check your current version:
Code:node -v - Hanapin yung patched version para sa line mo:
Nasa 20, 25, o mas luma ka pa? End-of-life na yan, so walang ρá†ch na darating. Plan your move to 22, 24, or 26.Code:22.x → 22.23.4 24.x → 24.22.1 26.x → 26.12.1 - Upgrade. If you use nvm, palitan lang yung version para sa line mo:
Official installer? Download the new one from the official site (link sa baba). Installed via apt, dnf, or another distro package manager? Yung distro mo ang naglalabas ng sarili nilang ρá†ch, so check their security updates.Code:nvm install 24.22.1 nvm use 24.22.1 - Docker: update the base image tag sa Dockerfile mo (e.g.,
node:24.22.1, or the same version with your-alpineor-slimvariant), then rebuild and redeploy. Check muna sa Docker Hub kung live na yung tag. Kung floating tag gamit mo likenode:24, rebuild withdocker build --pullpara di yung cached old image yung magamit. - CI/CD: check the Node version your pipelines use (e.g.,
node-versionsa GitHub Actions, or your.nvmrc) para di bumalik sa old version yung builds. - Restart every running Node process, then confirm sa production:
Code:node -v
Ano yung na-fix
| CVE | Issue | Severity | Lines |
|---|---|---|---|
| CVE-2026-111497 | Brotli decoder out-of-bounds write, can lead to remote code execution | High | 22, 24, 26 |
| CVE-2026-105482 | dns.resolve cuts off names that contain a NUL character | High | 22, 24, 26 |
| CVE-2026-106069 | TLS cert hostname bypass when the host loosely resolves to an IP | High | 22, 24, 26 |
| CVE-2026-105483 | TLS cert hostname bypass when the IP uses fullwidth digits | High | 24, 26 |
| CVE-2026-105481 | Keep-alive socket can process a response written before the request was sent | Medium | 22, 24, 26 |
| CVE-2026-106072 | Cert validation issue with non-canonical IPv4 hostnames | Medium | 22, 24, 26 |
| CVE-2026-106074 | crypto.randomUUID() and randomInt() repeat the same values across processes when built from startup snapshots or SEAs | Medium | 22, 24, 26 |
| CVE-2026-106073 | Permission Model bypass via fs.realpathSync | Low | 22, 24, 26 |
| CVE-2026-106070 | ZipFile returns attacker-controlled bytes after a failed header check | Low | 26 |
| CVE-2026-106071 | Permission Model gives too much file access via wildcard lookup | Low | 26 |
Plus dependency updates: c-ares, Undici, at root CA certs (dahil sa eMudhra intermediate CA compromise) sa lahat ng lines, OpenSSL sa 22 at 24, at SQLite sa 22.
Interesting detail: sa advisory credits, OpenAI Codex Security (Khai Tran at Sylvie Mayer) yung nag-report ng Brotli bug, at sina mcollina at aduh95 yung nag-fix.
Take note
- Konti pa lang yung technical details sa advisory, mostly titles at affected lines lang. Based sa title, nasa Brotli decompression yung bug, so mas exposed yung apps na nagde-decompress ng Brotli data galing sa labas. Still, ρá†ch na agad, wag nang hintayin yung full details.
- Yung randomUUID()/randomInt() issue, relevant lang kung gumagawa ka ng user-land startup snapshots o Single Executable Applications (SEA), based sa advisory.
- Two of the low-severity issues only matter kung gamit mo yung Permission Model.
- Yung TLS fixes, nire-reject na yung ilang non-canonical IP address formats (based sa release notes), so test muna sa staging bago i-push sa production.
- Based sa official Node.js EOL page, EOL na yung 20 at 25, pati yung mas luma. Apektado palagi yung EOL versions tuwing may security release, pero di na sila nakakakuha ng fix.
 Saan makukuha
You do not have permission to view the full content of this post. Log in or register now.
 Help desk
Nakapag-upgrade ka na? Pa-share kung smooth o may nasira, para alam ng iba kung ano yung aabangan:
Code:
From → to (version):
Install method (nvm/installer/apt/Docker):
OS:
Error, kung meron (exact message):
Bago mag-paste ng logs, tanggalin muna yung private hostnames, file paths, at tokens.
Yung mga helpful na reports at fixes, isasama ko sa main post para di na mag-scroll yung iba.
Notes at disclaimer
Hindi ako part ng Node.js project at hindi ako affiliated sa kanila. Galing sa official Node.js security advisory at EOL page yung info dito (checked October 23, 2026), kaya pwedeng magbago o madagdagan pa yung details. Di ko pa personally na-try yung upgrade, share ko lang based sa official info. Para sa pag-secure ng sarili mong apps at servers lang 'to. Test muna sa staging bago mag-deploy sa production, follow niyo yung license at terms ng Node.js, and use at your own risk.
 Sources & Credits
- Developer: The Node.js Project (nodejs on GitHub), OpenJS Foundation
- Source: Node.js blog, "Wednesday, October 21, 2026 Security Releases," checked October 23, 2026
- References: Node.js End-Of-Life page, checked October 23, 2026 · v22.23.4 release notes sa nodejs/node GitHub
- Image: Advisory screenshot: OpenJS Foundation and Node.js contributors, from the official Node.js blog
- Diagram: Made for this thread, based sa October 21, 2026 advisory
- Reporters at fixers: Brotli bug reported by OpenAI Codex Security (Khai Tran, Sylvie Mayer), fixed by mcollina at aduh95. Full list per CVE nasa advisory.