๐Ÿ”’ Closed 50-Day Premium SSH (United States)

Status
Not open for further replies.

Soul Calibre

เผ’ั‚ะฝั” ั‚ั”ัะผฮนฮทฮฑั‚ฯƒัเผ’
Contributor
Host IP: 35.247.130.127


Username: soulcalibre-0
Password: JBayudang03

Username: soulcalibre-1
Password: JBayudang03

Username: soulcalibre-2
Password: JBayudang03

Username: soulcalibre-3
Password: JBayudang03

Username: soulcalibre-4
Password: JBayudang03

You can change the password by running a terminal command:
Code:
passwd

  • Type the "Current Password" then hit "enter"
  • Type your preferred password then "enter"
  • Retype your preferred password then "enter"
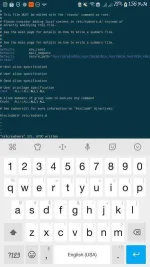
 
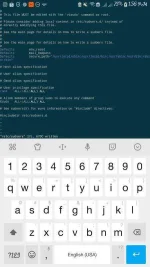
useless rin hindi makapasok sa root
If you can only tell me what's the right code or command to write in the file /etc/sudoers to limit what other users can, then I will add those users to sudoers group.
Screenshot-20190524-135622-Juice-SSH.webp
 
Kapag palitan mo naman yung...
%sudo ALL=(ALL:ALL) ALL

Mawawalan totally ng permission ang mga nasa sudoers group.
 
pa add na lang po ako sa sudo
I can't do that hanggat hindi ko ma-limitahan ang mga kayang i-run ng mga sudoers. Kasi kapag nasa sudoers group ka na, maa-access and kaya mo nang i-run lahat. Which is not good when it comes to management.
 
kung mag install ako damay ba lahat ng sudoers?
Hindi naman sa madadamay ang ibang users. Yun nga lang ay kapag nasa sudoers group ka na, you can access everything as "root". You can delete every user including the "root" user since you've gain access. That is what I wanted to avoid. If only someone can tell me the exact code or command para hindi ma-access ng sudoers ang mga critical commands, why not i-add lahay sa sudoers group, diba?
 
Status
Not open for further replies.

About this Thread

  • 34
    Replies
  • 289
    Views
  • 8
    Participants
Last reply from:
JhoeReek

Trending Topics

Online now

Members online
462
Guests online
9,409
Total visitors
9,871

Forum statistics

Threads
2,347,466
Posts
29,353,633
Members
1,097,959
Latest member
techsupport2011
Back
Top